

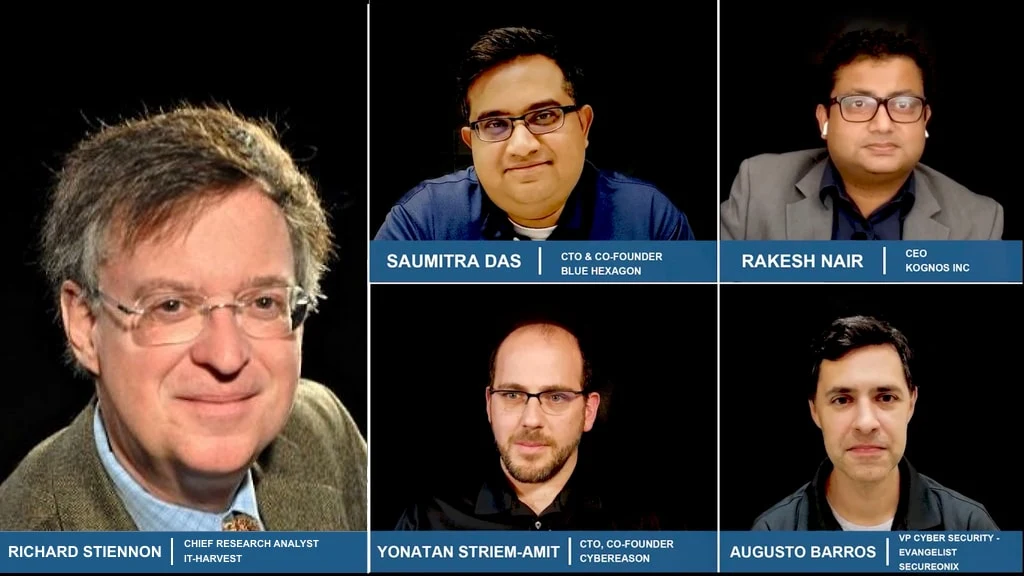
Your deployed agent is only as secure as its third-party plugins, foundational open-source models, and connected enterprise APIs. This eye-opening session dissects hidden vulnerabilities within the broader agentic ecosystem, focusing heavily on dependency risks and unauthorized data-leakage vectors. Learn how to comprehensively map, audit, and secure your automated software supply chain against sophisticated upstream exploitation.
Led by Richard Stiennon Chief Research Analyst, IT-Harvest No product pitches
Opening the floor…
Post Your Comments
Jump into the live discussion — no account needed. Say it, send it, it’s on the floor instantly.